gbhackers.com·19 november 2026
Hackers Hide Malware Inside Cheap TV Boxes to Steal Home Internet Bandwidth and Generate Fake Ads
ad fraud
Android TV
BADBOX 3.0
malware
MITRE ATT&CK
residential proxy
gbhackers.com
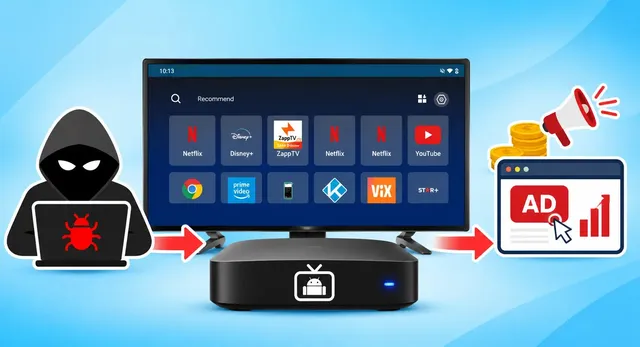
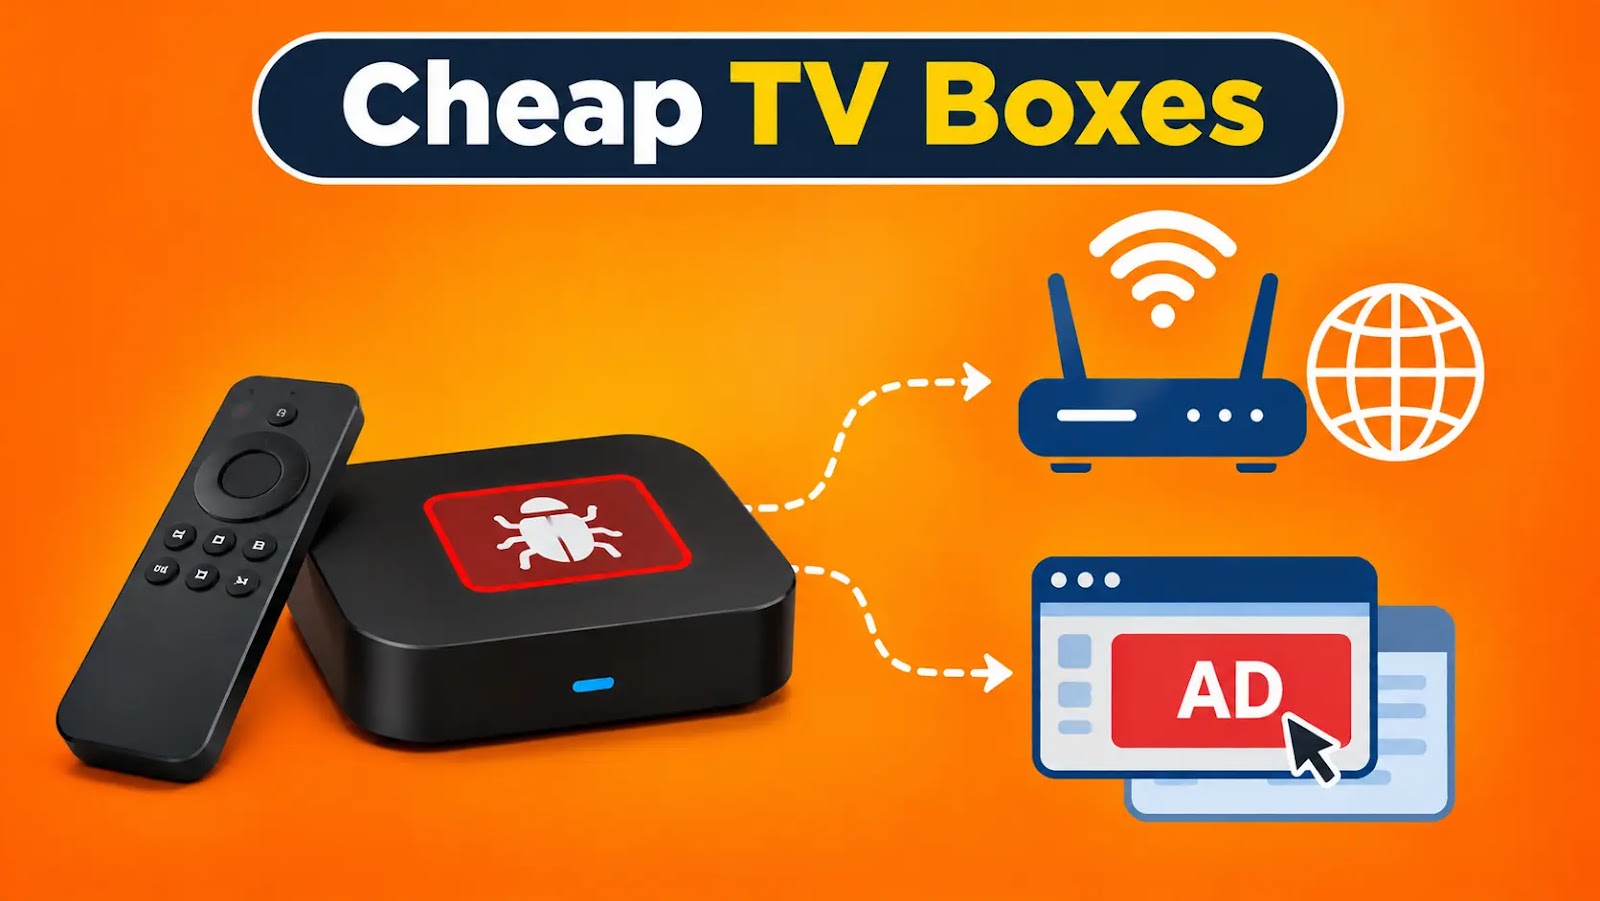
The BADBOX 3.0 operation turned inexpensive, uncertified streaming boxes into hidden video ad players and residential proxies, generating 40 billion bid requests per day at its peak. Researchers traced the backdoor and proxy modules to Chinese electronics manufacturer TXCZ and linked it to prior campaigns including BADBOX 2.0 and Triada-based firmware backdoors. Compromised devices secretly loaded modules to forward third-party traffic and execute invisible ad fraud across 11 residential proxy networks. Google recommends verifying Play Protect certification when choosing Android TV devices to mitigate these unconsented proxy enrollments.