bleepingcomputer.com·21 november 2026
BADBOX 3.0 botnet returns with record-breaking 40 billion daily ad requests
ad fraud
ad-fraud operation
Android devices
Android TV box
BADBOX malware
cybercrime
fraudulent advertising
fraudulent traffic
Google Play
HUMAN Satori
malware botnet
PXYEDGE
residential proxy networks
server-side ad insertion
bleepingcomputer.com
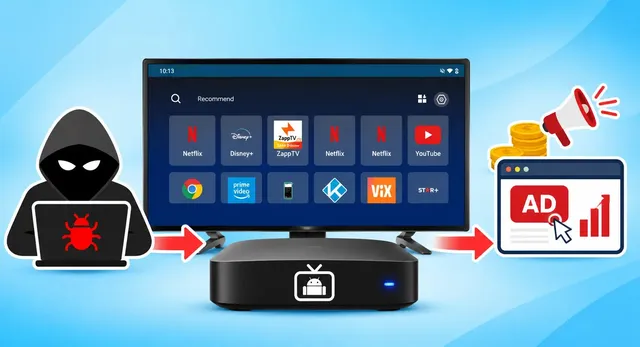
The BADBOX malware botnet has returned, generating a record 40 billion fraudulent advertising bid requests per day through infected Android-based devices. HUMAN's Satori researchers identified BADBOX 3.0 as the largest documented ad-fraud operation by daily bid request volume. The malware infects cheap Android devices, performing ad fraud and traffic proxying, and has been linked to a specific Chinese electronics manufacturer. HUMAN and Google have disrupted parts of the botnet, but operators are likely to adapt and continue their activities.