cybersecuritynews.com·19 november 2026
BADBOX 3.0 Malware Infects Android TV Boxes to Generate 40 Billion Fraudulent Ad Requests Daily

ad fraud
advertising bid requests
advertising fraud
Android streaming boxes
Android TV
BADBOX 3.0
botnet
command-and-control server
CTV traffic
FBI advisory
HUMAN Security
Play Protect
residential proxy networks
TXCZ
Vo1d botnet
cybersecuritynews.com
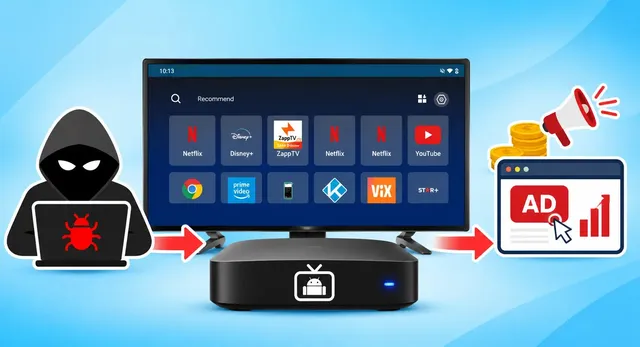
Low-cost Android streaming boxes powered an advertising fraud operation, BADBOX 3.0, generating 40 billion bid requests daily at its peak. The campaign used infected devices to play hidden video ads while mimicking legitimate streaming apps. Researchers from HUMAN Security's Satori Threat Intelligence and Research Team identified and disrupted BADBOX 3.0, publishing findings on November 18, 2026. The affected boxes ran the Android Open Source Project and were not Play Protect certified. The malware could also enroll boxes in residential proxy networks without consent, posing risks beyond streaming.