bleepingcomputer.com·30 october 2026
Critical Linux kernel flaw allows remote root attacks on MPTCP servers
Amazon Linux
Anthropic
CIQ
Claude AI
CVE-2026-98432
Debian
Go 1.24
Linux kernel
macOS
Multipath TCP
Oracle Linux
race condition
Red Hat Enterprise Linux
remote code execution
Rocky Linux
SUSE
Ubuntu
use-after-free
XNU
bleepingcomputer.com
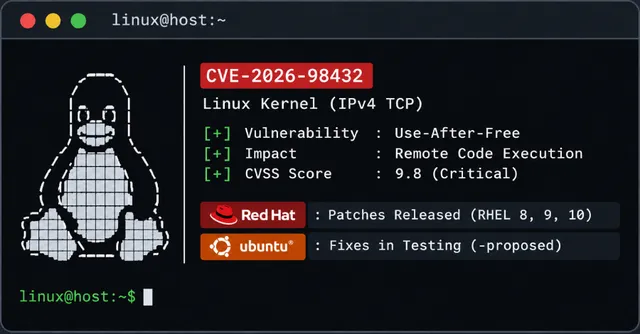
Security researchers at Anthropic developed an exploit for CVE-2026-98432, a critical Linux kernel vulnerability allowing unauthenticated remote code execution on servers with Multipath TCP (MPTCP) listeners. The flaw, scoring 9.8 out of 10, affects Linux kernels since version 4.4, including Ubuntu, Red Hat Enterprise Linux, and Rocky Linux. Anthropic demonstrated remote root code execution in 53 minutes using an unreleased Claude AI model. Patches are being rolled out, but some distributions like Ubuntu and RHEL remain vulnerable.