csoonline.com·30 october 2026
Anthropic AI model finds Linux kernel bug that leads to remote root access

Amazon Linux
Anthropic
Claude
CVE-2026-98432
Debian
Kernel Address Space Layout Randomization (KASLR)
Linux kernel
Multipath TCP (MPTCP)
Oracle Linux
Red Hat Enterprise Linux
remote code execution
SUSE
Ubuntu
use-after-free (UAF) bug
zero-click exploit
csoonline.com
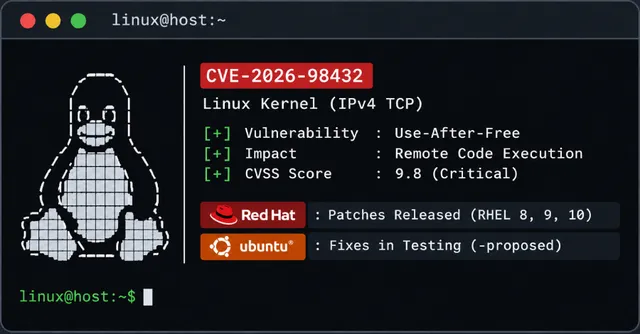
Anthropic discovered a critical Linux kernel vulnerability (CVE-2026-98432) in Multipath TCP (MPTCP) that allows remote root access. The zero-click exploit, developed with an unreleased Claude model, enables unauthenticated attackers to execute arbitrary commands. The flaw, a race-condition-induced use-after-free bug, affects multiple Linux kernel branches and has a severity score of 9.8. Fixed releases are available, but some distributions like Ubuntu and Red Hat Enterprise Linux have yet to patch.