gbhackers.com·19 november 2026
Hackers Exploit Critical RCE Vulnerabilities in Synology NAS, Apache Axis and REDCap, CISA Warns
Apache Axis
C3RB3R
CISA
CVE-2024-10441
CVE-2026-40217
CVE-2026-90436
CVE-2026-90817
federal remediation deadlines
LiteLLM
ransomware
REDCap
remote code execution
Synology
vulnerabilities
gbhackers.com
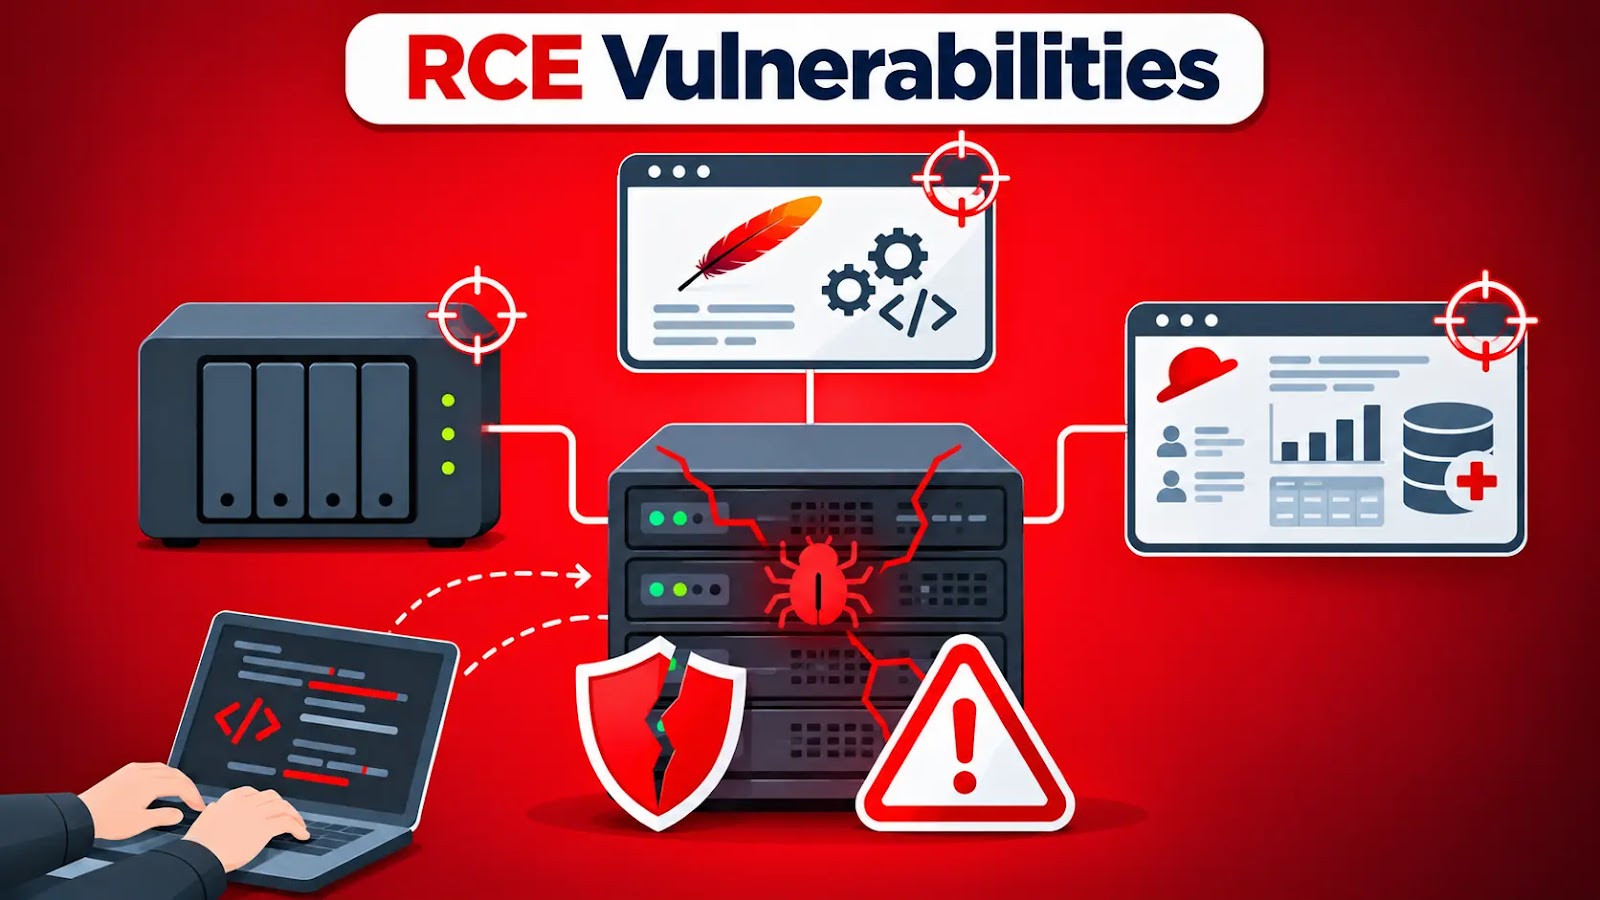
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on November 18, 2026, including CVE-2024-10441 in Synology’s system plugin daemon and CVE-2026-90436 in Apache Axis. The vulnerabilities enable remote code execution and affect various systems, including Synology DiskStation Manager, Apache Axis, and Vanderbilt University’s REDCap platform. CISA set federal remediation deadlines for these vulnerabilities, with November 21 for Synology DSM, Apache Axis, and REDCap, and December 2 for LiteLLM. Organizations are encouraged to prioritize remediation and preserve evidence before patching where feasible.