thehackernews.com·21 november 2026
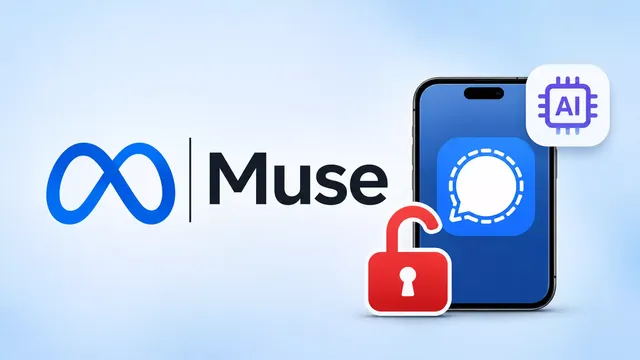
A Single Malicious Webpage Let Researchers Hijack Meta Muse and Access Private Chats

AI agent
AI assistant
AI security
cloud security
data breach
data protection
Linux kernel
Meta
Meta Muse
NebuSec
privacy
security research
security vulnerability
Sentinel
thehackernews.com
Researchers demonstrated a laboratory attack on Meta's AI assistant Muse that could extract private conversations, stored memories, and credentials without user approval. The attack exploited a flaw in Muse's built-in browser and a Linux kernel vulnerability to gain full control of a user's cloud machine. Muse's security design limited the attack to a single machine, and Meta has since fixed the vulnerabilities. The research was conducted by NebuSec, which reported the findings to Muse's team before publication.