cyberpress.org·19 november 2026
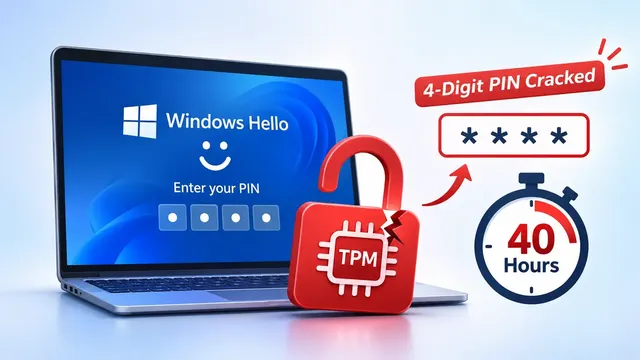
Windows Hello Vulnerability Lets Attackers Brute-Force PINs in Just 40 Hours

AMD
BitLocker
firmware TPM
hardware configuration
HMAC authentication
incident response
Intel
Pluton
Replay Protected Monotonic Counters
Single Sign-On
SPI flash
Trusted Platform Module
Windows 11
Windows Hello
Windows Hello for Business
cyberpress.org
A newly disclosed Windows Hello PIN vulnerability was cracked in 40 hours on a locked, encrypted Windows system by bypassing the Trusted Platform Module’s anti-hammering protection. The flaw affects firmware TPM implementations and can undermine the integrity of the state that enforces the guessing limit. The researchers also found that the same rollback weakness affected BitLocker’s TPM-backed pre-boot protection when configured with a startup PIN. The findings highlight the importance of hardware configuration in incident response and the need to verify physical-tamper resistance for lost or seized systems.